Best Enterprise Data Security Platform For Ransomware Recovery
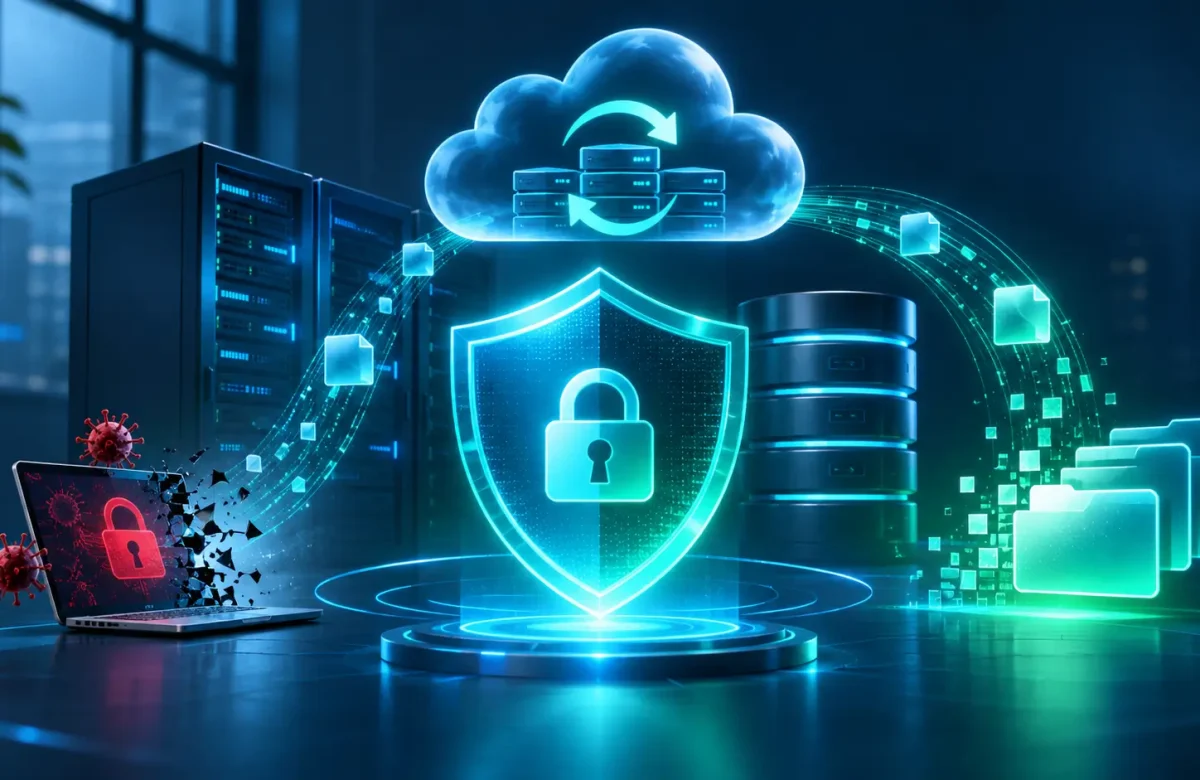
Ransomware attacks can disrupt business operations, compromise sensitive information, and make critical systems inaccessible. For organizations that depend on digital infrastructure, having a reliable recovery strategy is essential to maintaining business continuity and protecting valuable data.
Choosing the right Data Security Platform can help businesses strengthen their cybersecurity defenses, monitor potential threats, protect endpoints, and maintain secure backups that support recovery after an incident.
However, effective ransomware protection requires more than installing security software. Businesses need a comprehensive approach that combines endpoint protection, network security, cloud security, backup solutions, and disaster recovery planning.
For companies in Egypt, working with an experienced IT solutions provider such as Arab Computers can help bring these technologies together into a security strategy aligned with business requirements.
What Is Ransomware Recovery?
Ransomware is malicious software that encrypts files or locks systems, then demands payment for the key to restore them. Ransomware recovery is the work of returning systems and data to a trusted, usable state afterward. It involves more than restoring files.
A typical recovery isolates infected devices, identifies how the attacker got in, removes the malware, confirms that backups are clean, restores systems in priority order, and closes the gap that allowed the intrusion.
Many teams assume recovery means “restore from backup.” That step matters, but a backup the attacker could reach may be encrypted too, and restoring it can bring the malware back. Effective recovery depends on several layers working together: prevention, detection, protected backups and a documented response process.
Why Is Ransomware Recovery Important for Businesses?
The most obvious cost is downtime. Operations stop, customers wait, and staff spend days rebuilding systems. Other costs follow: damaged customer trust, regulatory scrutiny, and the effort required to confirm whether data was copied or exposed. Businesses that handle personal or financial information must also explain how they protected it.
Planning changes how a team behaves during an incident. Teams that have rehearsed recovery act deliberately. Teams without a plan often feel pressure to pay, restore unverified backups, or reconnect infected machines too early. A documented process removes much of that guesswork.
Best Enterprise Data Security Platforms for Ransomware Recovery
No single product covers the full recovery cycle, so most enterprise environments combine tools from several vendors. The platforms below are widely used in this area. Their inclusion reflects common market use, not a ranking. The right combination depends on your environment, budget and team.
When comparing options, start with four questions:
- Can an attacker change or delete your backups?
- Can endpoint and network tools spot encryption activity early?
- Can you restore many systems quickly, and in the right order?
- Does the vendor’s support model match your team’s capacity?
Veeam
Veeam is known for backup and recovery software across virtual, physical and cloud workloads. Its immutable repository options keep backup copies unchanged for a set period, which helps protect them from tampering.
Sophos
Sophos offers endpoint protection, managed detection and response, and firewalls. Its anti-ransomware features watch for encryption behavior, and some can reverse changes made by suspicious processes.
Kaspersky
Kaspersky provides endpoint security with anti-ransomware components, plus incident response services. Some markets have restricted its products, so confirm the fit with your clients and procurement rules first.
Fortinet
Fortinet is best known for firewalls and network security appliances, with endpoint detection tools in its wider portfolio. Network segmentation and threat inspection can limit how far ransomware spreads.
Microsoft
Microsoft offers Defender for endpoint protection, Sentinel for security monitoring, and Azure Backup, which supports immutability settings for backup vaults. Organizations already running Windows Server, Microsoft 365 or Azure often find the integration practical.
Cisco
Cisco’s portfolio spans firewalls, endpoint protection, email and web security, and threat intelligence, with security analytics through Splunk. Its main contribution to recovery is visibility into what was affected and how it moved.
Dell Technologies
Dell’s PowerProtect Cyber Recovery keeps copies of critical data in an isolated vault separate from the production network. An attacker who reaches production systems cannot easily reach the vault.
When Does Your Business Need Ransomware Recovery?
Any organization that holds data it cannot afford to lose needs a recovery capability. The need becomes more urgent in several situations:
- Downtime is expensive: Call centers, online services, clinics and logistics operations lose revenue or service quickly when systems stop.
- Your data carries legal duties: Egypt’s Personal Data Protection Law (Law No. 151 of 2020) imposes obligations on organizations that handle personal data, including certain breach-reporting requirements. Confirm the specifics with your legal adviser.
- Backups share the production network: If backup storage is always reachable from core systems, an attacker may reach it too.
- The environment has grown: Multiple sites, cloud services and a VoIP phone system create dependencies that a simple restore procedure may not cover.
- Restores have never been tested: A backup that has never been restored is an assumption, not a plan.
If several of these apply, a recovery plan belongs on the agenda now, not after an incident.
What Is a Ransomware Recovery Plan?
A ransomware recovery plan is a written, tested set of procedures for responding to an encryption attack. It names the people responsible for each step, ranks systems by business importance and defines how each one will be restored and verified.
A useful plan usually covers six areas:
- Detection and containment: How staff report suspicious activity and how infected devices are isolated quickly.
- Assessment: Which systems are affected, how the attacker entered, and whether backups are intact.
- Communication: Who briefs management, staff, customers, regulators and law enforcement, and how decisions are recorded.
- Restoration: The order of recovery, using verified clean copies. Identity, email, accounting and phone services often come first.
- Verification and hardening: Scanning restored systems, resetting credentials, closing the entry point and watching for signs of return.
- Review: A written account of the incident and the plan updates it requires.
The plan should also settle the ransom payment question in advance. Payment does not guarantee decryption, and it can mark an organization as a repeat target. Name who holds that authority and what legal advice is required.
Finally, test the plan. Run a restore drill for at least one critical system on a regular schedule and record how long it takes. Finding out in a drill that a restore takes three days is far better than finding out during an incident.
What to Look for in a Ransomware Recovery Provider
Choosing a provider means deciding who will answer the phone at two in the morning. Start with two numbers: your recovery time objective (RTO), the longest a system can stay down, and your recovery point objective (RPO), the most data you can afford to lose.
Then evaluate providers on these areas:
- Experience: Ask for examples of recovery work with organizations of similar size and sector.
- Expertise: Confirm that engineers understand your mix of platforms, such as virtualized servers, file services, databases and VoIP systems.
- Communication: Ask who you will speak with during an incident, how often you will receive updates and who writes the final report.
- Technology: Look for protected or immutable backups, monitoring that flags unusual encryption activity and documented restore procedures.
- Customization: A 40-person accounting firm and a multi-site manufacturer face different risks. The plan should be built around your RTO and RPO, not a generic package.
- Reliability: Ask how the provider tests its own recovery procedures and how it staffs incident response.
- Customer support: Confirm support hours, escalation paths and after-hours availability.
Why Choose Arab Computers as Your Trusted Ransomware Recovery Partner?
Arab Computers is an IT solutions company based in Alexandria, Egypt, and has operated since 1986. Its service areas include network infrastructure and data center solutions, backup and virtualization, cloud services, endpoint solutions, network and security, VoIP systems and call centers, and surveillance.
That range is relevant to recovery because an attack rarely stays within one layer. It can reach the network, servers, endpoints, backup environment and phone systems at once. A provider working across those areas can account for how they depend on each other during the assessment phase.
If you want to discuss your environment, a consultation with the Arab Computers team is a practical place to start. You can ask which services fit your setup and what a recovery plan would need to cover.
FAQ
How Do You Recover from a Ransomware Attack?
Disconnect affected devices from the network without wiping them, so they can be investigated. Find how the attacker got in, confirm that backups are clean and restore systems in priority order. Before reconnecting anything, patch the entry point, reset credentials and check for persistence. Report the incident to your response contact and to the relevant authorities where required.
Is It Possible to Recover Files from Ransomware?
Often, but not always. Results depend on the ransomware variant, whether a working decryption tool exists and whether clean copies are available. Some security researchers publish free decryptors for certain families. Immutable or isolated backups are the most dependable route, and no provider can guarantee full recovery.
What Is the Best Solution for Ransomware?
There is no single best product for every organization. Effective protection combines prevention (endpoint security, patching and access control), detection (monitoring for encryption behavior) and recovery (protected backups that are tested regularly). The right mix depends on your environment and your team’s capacity to run it.